Enterprise trust
Trust the boundary because the product makes it visible.
DeepICE treats tenancy, authority, lifecycle, audit, learner visibility, provider readiness, and production acceptance as operating controls rather than marketing footnotes.
Operational boundaries
Six controls that stay attached to the work.
- 01Tenant
- Institutional records, relationships, branding, and access remain scoped to the authorized tenant.
- 02Authority
- The server rechecks capability and relationship boundaries before a governed action persists.
- 03Lifecycle
- Creation, review, approval, publication, assignment, and learner visibility remain separate states.
- 04Evidence
- Governed decisions and access changes retain the actor, action, time, and affected record.
- 05Learner visibility
- Private drafts are not learner-visible. Publication and assignment remain explicit gates.
- 06Provider readiness
- Meeting, chat, storage, email, and identity integrations are described as ready, configured, or unavailable - never implied.
Production readiness
A demonstration is not represented as a production posture.
Customer credentials, provider accounts, storage, identity, email, environment configuration, and cloud services remain explicit deployment decisions.
Production acceptance requires the agreed security, infrastructure, operational, and role-journey evidence for that customer scope.
Evidence before change
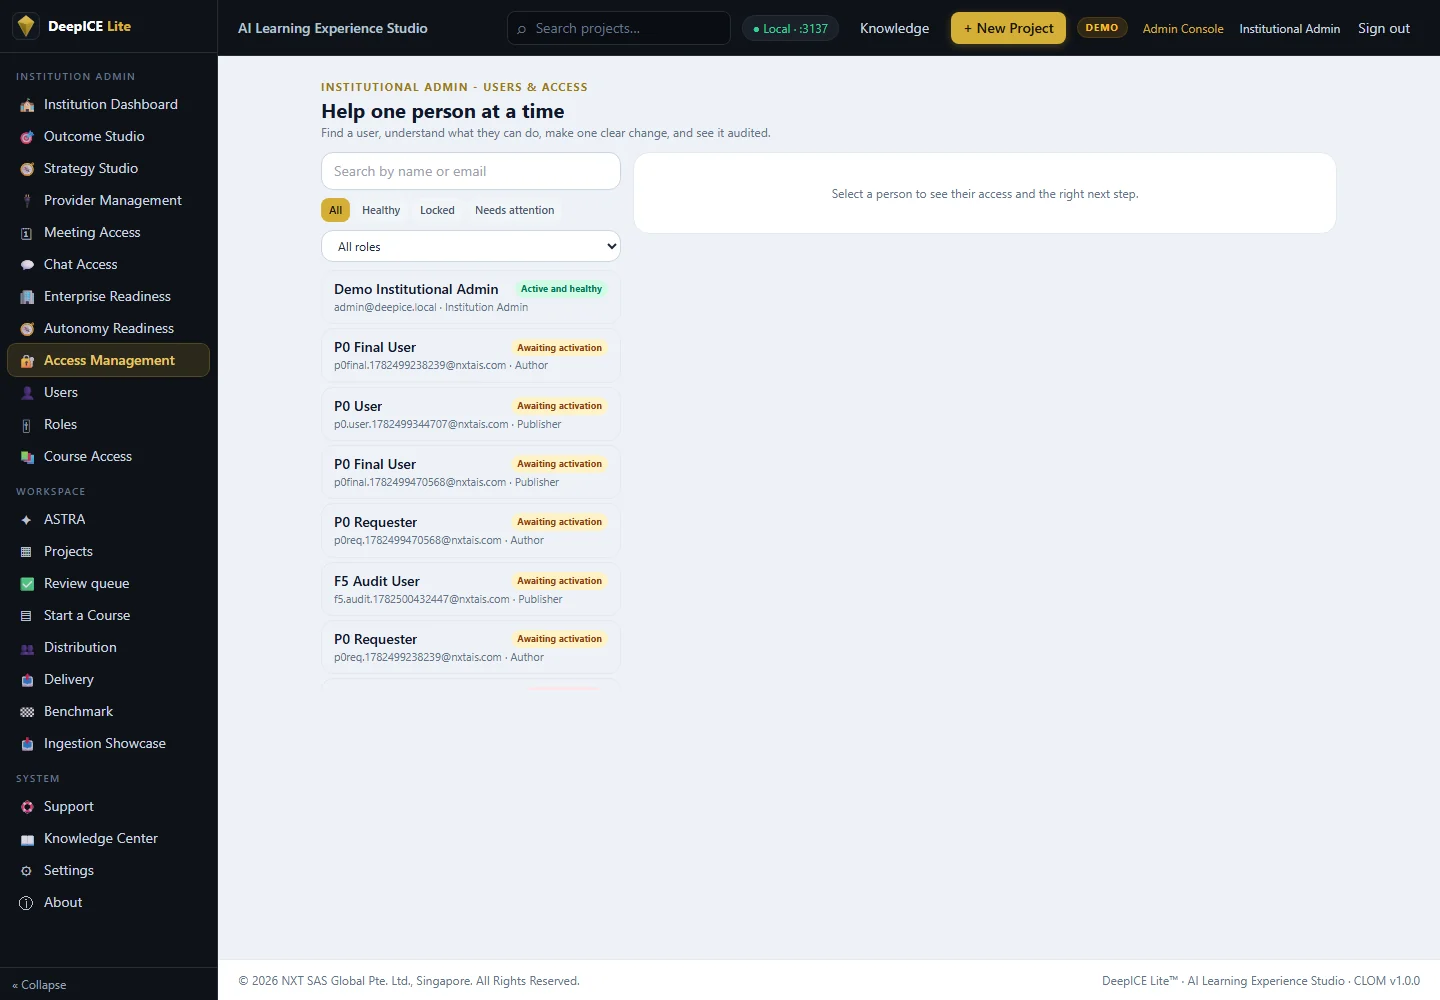
Administrators understand access before confirming it.
The workspace explains effective responsibility, delegated capability, account health, and the intended change before it reaches the existing audited authority path.
Request a guided demonstration
Review trust against your production requirements.
We will distinguish product capability, customer configuration, provider dependency, and production evidence.